Hosting, security, and compliance
Where Avanoo hosts data, who processes it, and which security and GDPR measures apply — for vendor reviews and DPOs.
This page covers residency, security measures, subprocessors, and compliance posture. For the data inventory itself, start with What Avanoo collects.
Hosting and residency
Avanoo is a multi-tenant SaaS. The application, databases, and backups run on Amazon Web Services in the European Economic Area:
- Primary: AWS Europe (Paris),
eu-west-3 - Redundancy: AWS Europe (Frankfurt),
eu-central-1
Customer data is stored and processed in these EU regions. Standard service delivery does not transfer usage data outside the EEA. Failover between Paris and Frankfurt is documented and manual.
Avanoo does not operate its own datacenter. There is no OVH or Google Cloud hosting path for the production service.
AI inference for the optional in-product assistant uses AWS Bedrock in the EU only.
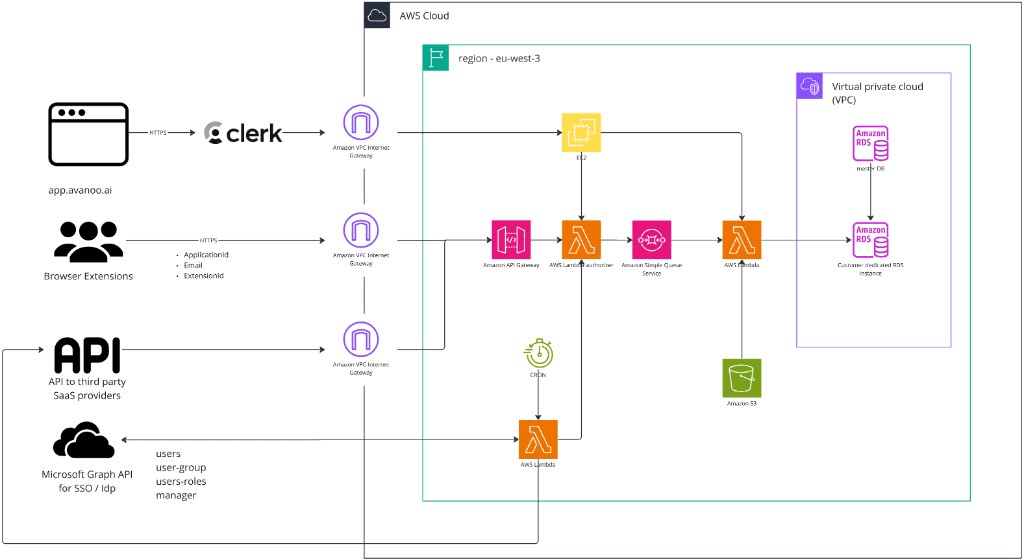
The diagram below is the production architecture in the primary Paris region. Frankfurt is used for redundancy and is not shown.
Encryption and keys
| Layer | Measure |
|---|---|
| In transit | TLS 1.2 or higher. Certificates issued and renewed through AWS Certificate Manager |
| At rest | AES-256 on RDS (PostgreSQL) and S3 (SSE-S3 or SSE-KMS) |
| Keys | AWS KMS, no local key handling, access restricted and logged |
| Backups | Encrypted RDS snapshots (7-day default) and versioned S3 objects, with periodic restore tests |
Isolation and access
- Customer environments are logically isolated in the database and in logs. There is no application-level mixing of tenant data.
- Dashboard access uses named accounts through SSO, with three roles: Read, Analyst, and Admin. Multi-factor authentication is enforced by the customer’s identity provider.
- Avanoo staff access follows least privilege, named IAM accounts with MFA, and AWS SSO. Direct database access is forbidden except for maintenance.
- Access to data, failed access, and suspicious behaviour are logged (AWS CloudTrail and GuardDuty). Logs are kept at least 12 months.
Subprocessors
Distinguish three things that vendor questionnaires often mix up.
Processors of customer data in the service
| Subprocessor | Role | Location |
|---|---|---|
| Amazon Web Services | Hosts the application, databases, object storage, and backups | EEA (Paris, Frankfurt) |
| Clerk | Authenticates administrators of the Avanoo dashboard (SAML, OIDC, SCIM) | See the DPA annex. Clerk does not identify employees in the browser extension |
| AWS Bedrock | Optional in-product assistant | EU region only |
The contractual list, retention, and notice period for changes are in the Data Processing Agreement annex. Avanoo notifies customers before adding or replacing a subprocessor.
Transfers outside the EEA, if any, use GDPR-appropriate safeguards such as the European Commission’s standard contractual clauses.
Not Avanoo subprocessors
- Your identity providers (Microsoft Entra, Google Workspace, Okta, and others) remain your systems. Connecting them is optional and under your control.
- GitHub is Avanoo’s source control. It does not host customer tenant data.
- Google Workspace and Vanta are Avanoo internal collaboration and compliance tooling. They are not used to process your employees’ usage events.
GDPR
| Topic | Position |
|---|---|
| Roles | Customer = controller. Avanoo = processor (DPA, GDPR Article 28) |
| DPO | External DPO (law firm Acmai). Contact privacy@avanoo.ai or dpo@avanoo.ai |
| Security contact | security@avanoo.ai (CISO) |
| Minimisation | Metadata only; allowlist; per-capability switches off by default; see What Avanoo collects |
| Employee information, DPIA, works council | Customer responsibility. Avanoo provides the inventory and assistance |
| Breach notification | Avanoo notifies the customer as soon as possible by email and cooperates under Articles 33 and 34 |
| End of contract | One month to request return or destruction; otherwise destruction within one year of the DPA ending |
Avanoo is a French company: Avanoo SAS, 54 rue du Faubourg Poissonnière, 75010 Paris, SIREN 925 197 519.
Certifications
Avanoo does not currently hold ISO 27001, ISO 27701, SOC 2, SecNumCloud, or HDS certification of its own service.
What is in place:
- A documented information-security policy (PSSI), available as a PDF on request.
- Independent external penetration testing.
- Internal security reviews.
- An ISO/IEC 27001 programme (tooling via Vanta), with certification targeted for 2027. SOC 2 tracking is in the same programme; Avanoo is not SOC 2 certified today.
- Hosting on AWS, which holds its own ISO 27001, SOC, and (in France) HDS attestations. Infrastructure questions about HDS or SecNumCloud therefore refer to the hosting provider, not to Avanoo’s application.
Continuity
Backups are automated and encrypted. Restore tests are periodic. A continuity and recovery plan covers failover between Paris and Frankfurt, with annual crisis exercises.
Documents available on request
Share these with a prospect, DPO, or works council rather than paraphrasing them:
- Data Processing Agreement (processor contract, including the subprocessor annex)
- This documentation: What Avanoo collects and this page
- Privacy policy: avanoo.ai/legal/privacy-policy
- Information-security policy (PSSI) and security-assurance plan
- External penetration-test report, under NDA
- Works-council briefing template, when the deployment is in France
For a feature-specific setting (which switches are on in a given tenant), the customer administrator exports the configuration from the platform, or asks their Avanoo representative.